Low Severity
Published: Nov 6, 2026
Cut through vulnerability alert noise. Surface the signal. Triages npm/pip/trivy/grype/dependabot/snyk alerts in seconds.
# depquiet
[](https://github.com/samuelrojas-dev/depquiet/actions/workflows/ci.yml)
[](https://pypi.org/project/depquiet/)
[](https://pypi.org/project/depquiet/)
[](https://github.com/samuelrojas-dev/depquiet/blob/main/LICENSE)
[](https://codecov.io/gh/samuelrojas-dev/depquiet)
**Cut through vulnerability alert noise. Surface the signal.**
`depquiet` triages your `npm audit` / `pip-audit` / `trivy` / `grype` / Dependabot / Snyk alerts and tells you which CVEs actually matter — in seconds, not hours. It can also **scan lockfiles directly** using the [OSV.dev](https://osv.dev) API — no external scanner required.
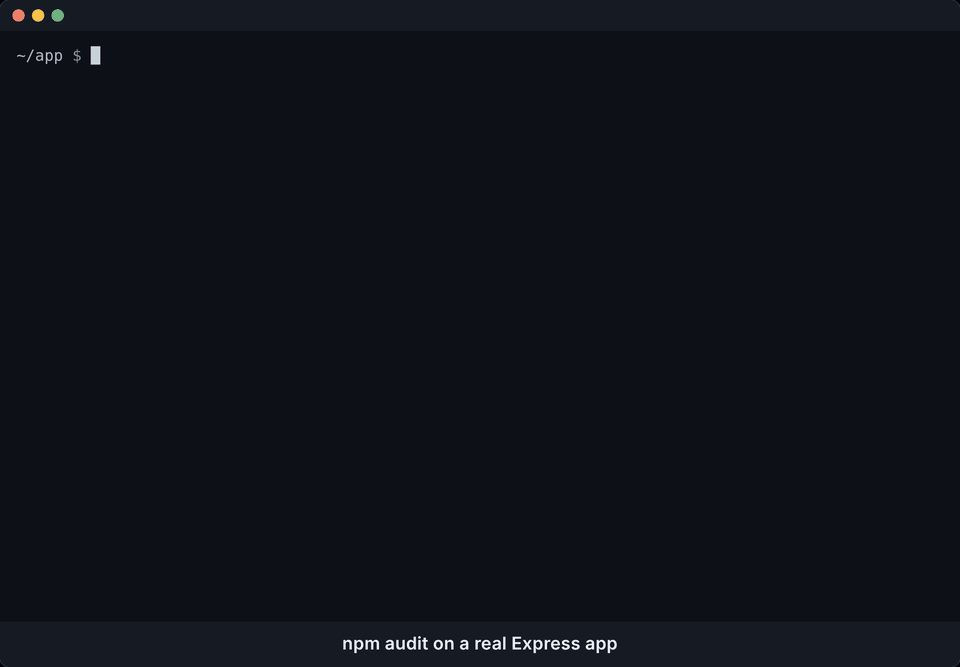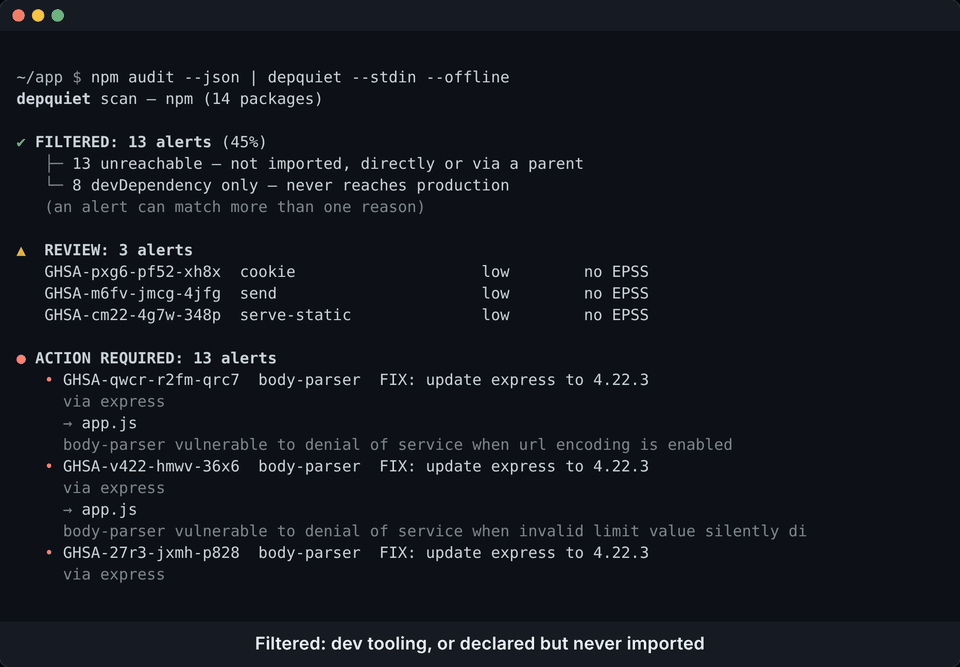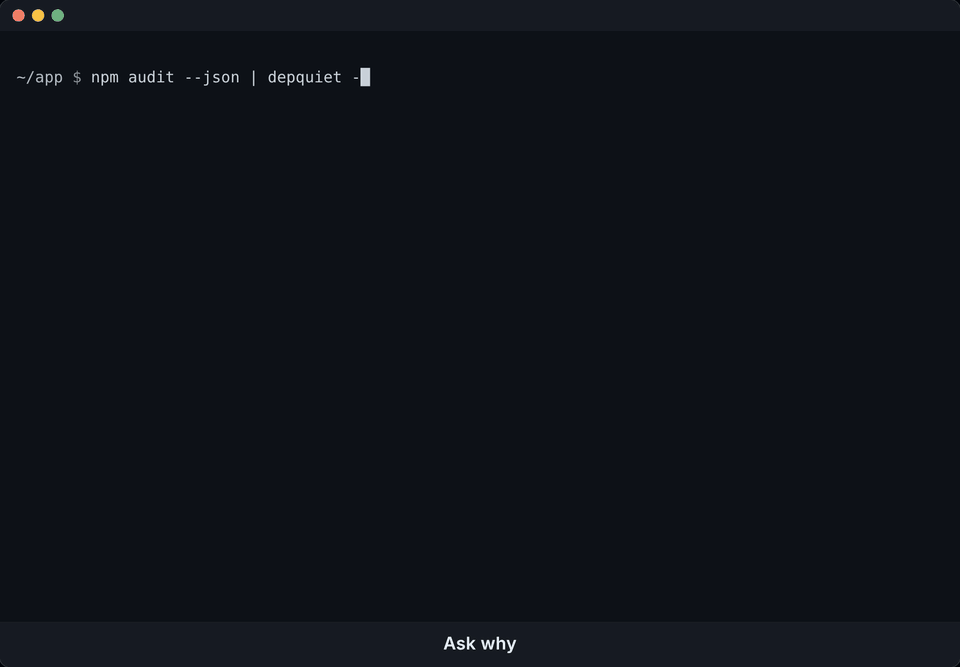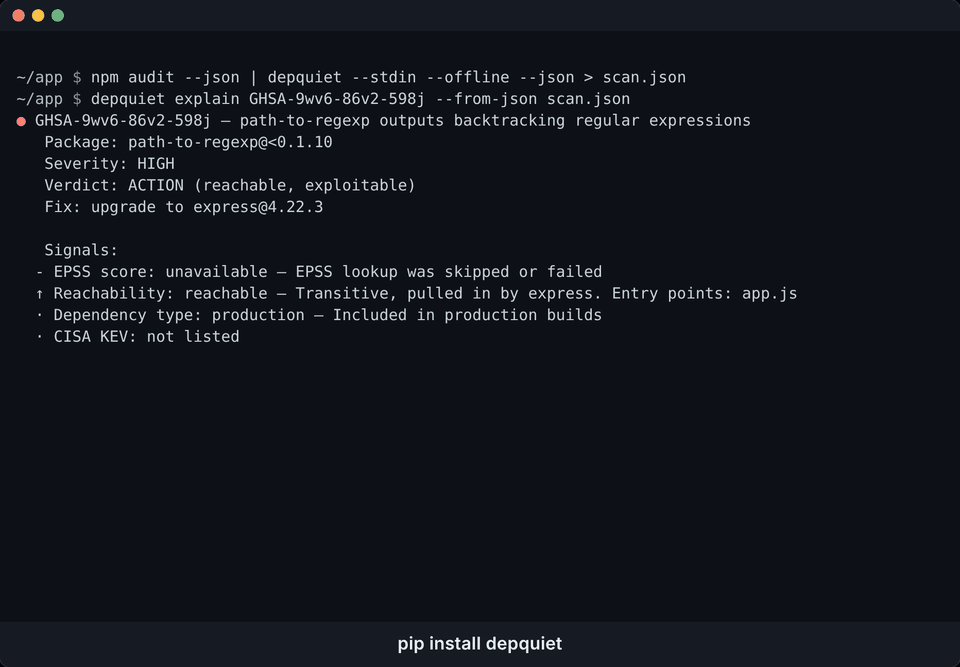
Every line in the recording is real command output ([how it's made](https://github.com/samuelrojas-dev/depquiet/blob/main/docs/demo/make_demo.py)).
The same run as text ([reproduce it](https://github.com/samuelrojas-dev/depquiet/blob/main/benchmarks/RESULTS.md#real-npm-express)):
```
$ npm audit --json | depquiet --stdin
depquiet scan — npm (14 packages)
✅ FILTERED: 13 alerts (45%)
├─ 13 unreachable — not imported, directly or via a parent
└─ 8 devDependency only — never reaches production
(an alert can match more than one reason)
⚠️ REVIEW: 3 alerts
GHSA-pxg6-pf52-xh8x cookie low no EPSS
...
🔴 ACTION REQUIRED: 13 alerts
• GHSA-9wv6-86v2-598j path-to-regexp FIX: update express to 4.22.3
via express
→ app.js
path-to-regexp outputs backtracking regular expressions
...
Total: 29 aler